
REST APIs to MCP Tools with Google Cloud API Gateway
Many organizations already expose important capabilities through REST APIs. For AI agents to use them, they need shared tool descriptions and calling conventions. Google Cloud API Gateway adds an option for an existing gateway to act as a remote MCP server without building an entirely new intermediary.
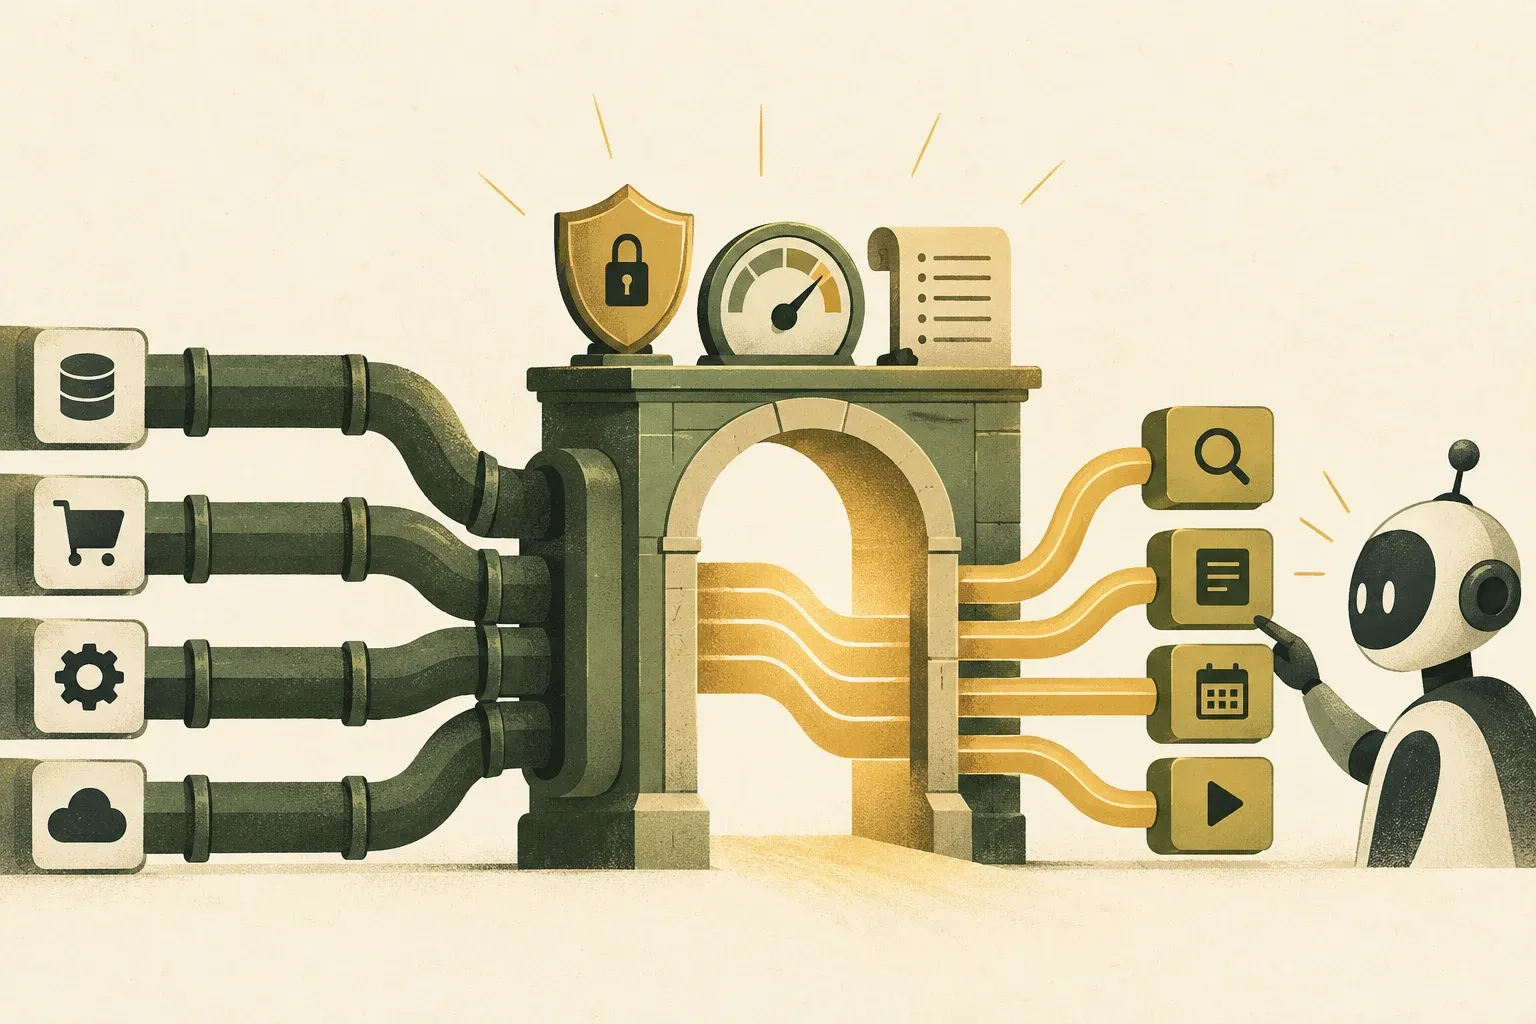
API Gateway translates MCP requests to the existing REST API
Model Context Protocol (MCP) defines how agents discover and invoke tools. Google Cloud API Gateway can receive JSON-RPC MCP requests at a single endpoint and convert tools/call into a REST request, then converts the response into an MCP result
Converted requests still use the original operation’s authentication, quotas, and logging. Teams can avoid building a separate MCP server that duplicates routing and policies. The feature is in Public Preview; assess stability and requirements before critical use.
Start with OpenAPI 3 and descriptions the model can understand
To enable it, you must use OpenAPI 3.0.x or 3.1.x and add a document-level annotation to enable MCP. Then specify whether each operation will be used as a tool or not. Each operation must have a backend and a non-empty description.
Tool descriptions are a main signal for model selection. Explain what the tool does, when to use it, and its limits. Broad names such as “Manage data” may lead to wrong tool choices or unintended arguments.
Secure tool discovery separately from execution
When an agent calls a tool, the gateway uses JWT or API keys as defined for the REST operation. Quotas and logs follow normal traffic paths. However, tools/list which exposes tool names and input schemas, is not protected by default according to the announcement
Production systems should also consider requiring JWT for discovery: even without operation access, tool lists and schemas may reveal architecture or attack-planning information. API keys cannot protect tools/list in the form Google describes
Exposing APIs to agents adds risks of actions diverging from intent
Traditional REST APIs follow relatively fixed code paths, while agents choose tools from language and context vulnerable to prompt injection or misunderstanding. Authentication identifies the caller; it does not establish alignment with user intent.
- Grant minimum permissions: Separate agent credentials and enable only necessary operations
- Limit effects: Use quotas, validation, and idempotency for data changes
- Request approval: Jobs that pay money, delete data, or send messages should have a confirmation step where details are visible.
- Traceability: Link user intent, tool calls, credentials, and results in logs. log should connect user intent, tool call, credential, and results together.
Not every API should become a tool
Start with low-impact read operations and clear schemas. Test tool selection, arguments, and error handling before adding writes under stricter policies. Internal APIs with broad endpoints or free-form commands should first be wrapped in a narrowly scoped service.
You should also check whether the error message or response contains secrets and personal information, because what the backend returns may be imported into the context of the model and appear in other logs.
Hypothetical test plan for your team's own API: Start with one read-only tool and nonconfidential test data. Check tool discovery separately from backend execution, using valid, missing, and unauthorized credentials. Unauthorized requests must not read data even if they can see the tool name. Then check Gateway and backend logs and quotas before adding write tools. This plan has not been run on Google Cloud and must not be tried on unauthorized APIs.
Define permissions and checks before exposing more tools
API Gateway lets agent tools use existing authentication, quotas, and logging. Before exposing more tools, inventory the APIs, select only necessary operations, write clear descriptions, and assess threats. Start with reads before expanding to operations that change real systems.
Sources
This article refers to Public Preview features of Google Cloud as of 7 October 2026. Behavior, pricing, limitations, and availability may change before General Availability. Check the latest documentation and test in an isolated environment.